• A significant cyberattack disrupted Nevada’s state government network on August 24, forcing all state office branches to shut down operations for 48 hours.

    The intrusion began with the exploitation of an unpatched VPN gateway, allowing the threat actor to gain initial foothold on the internal network.

    Within hours, the attackers deployed a custom malware payload designed to escalate privileges, move laterally across critical servers, and exfiltrate sensitive data.

    This event marks one of the most severe disruptions of state IT services in recent history, affecting email, public records access, and internal communication channels.

    Governor Lombardo Press Office analysts noted that the malware leveraged a multi-stage attack vector: a lightweight dropper written in PowerShell, which in turn fetched a second-stage binary from a compromised web server.

    This binary contained encrypted configuration files, indicating the attackers’ intent to remain undetected while mapping the network topology.

    As state technicians worked to isolate infected endpoints, normal user authentication services were rerouted to offline backups, further complicating the recovery process.

    Initial forensic analysis revealed that the dropper script used the following pattern to establish persistence on reboot:-

    $TaskAction = New-ScheduledTaskAction -Execute 'powershell.exe' -Argument '-NoProfile -WindowStyle Hidden -File C:\Windows\Temp\svc_update.ps1'
    $Trigger    = New-ScheduledTaskTrigger -AtStartup
    Register-ScheduledTask -TaskName 'WindowsUpdateSvc' -Action $TaskAction -Trigger $Trigger -Description 'System Update Service'
    Incident report (Source – X)

    This technique allowed the malware to relaunch silently, even after endpoint patches were applied.

    Governor Lombardo Press Office researchers identified the dropper’s code similarities to known APT toolkits, suggesting that the perpetrators possess advanced capabilities and extensive reconnaissance data on state infrastructure.

    Infection Mechanism

    Delving deeper into the infection mechanism, the second-stage binary employs a custom communications protocol over HTTPS, masquerading its traffic as benign REST API calls to evade intrusion detection systems.

    Upon execution, the binary loads a DLL into the Windows Management Instrumentation (WMI) host process (wmiprvse.exe), effectively concealing its operations within legitimate system processes.

    The DLL decrypts embedded payloads in memory, deploying modules that scan for domain controllers and file shares.

    Once targets are identified, encrypted archives of critical files are staged for exfiltration using chunked uploads to a remote C2 server.

    The malware transition from initial code execution to data exfiltration without triggering standard network security alarms.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Nevada IT Systems Hit by Cyberattack – State Office Closed for Two Days appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Data I/O Corporation, a well-known electronics firm that specializes in device programming and security provisioning solutions, revealed a ransomware attack that penetrated its internal IT infrastructure in a major cybersecurity event. The incident, detected on August 16, 2025, prompted an immediate activation of the company’s incident response protocols, highlighting the persistent threat of ransomware in […]

    The post Electronics Manufacturer Data I/O Suffers Ransomware Breach appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Cisco has issued a High-severity security advisory alerting customers to a critical vulnerability in the Intermediate System-to-Intermediate System (IS-IS) feature of NX-OS Software for Cisco Nexus 3000 and 9000 Series switches. 

    Tracked as CVE-2025-20241 with a CVSS base score of 7.4, the flaw could allow an unauthenticated, Layer 2-adjacent attacker to send a malformed IS-IS packet that restarts the IS-IS process, potentially reloading the device and causing a denial-of-service (DoS) condition

    Key Takeaways
    1. Cisco Nexus 3000/9000 IS-IS flaw allows adjacent DoS.
    2 No workaround; enable IS-IS area authentication.
    3. Apply Cisco’s free NX-OS update.

    Cisco Nexus 3000 and 9000 Vulnerabilities

    The vulnerability stems from insufficient input validation when parsing ingress IS-IS packets. An attacker must be on the same broadcast domain as the target switch and can exploit the flaw by transmitting a specially crafted IS-IS L1 or L2 packet. 

    Upon receipt, the NX-OS IS-IS daemon may crash and subsequently reload the entire switch, disrupting network routing and traffic forwarding. This condition affects:

    • Cisco Nexus 3000 Series Switches
    • Cisco Nexus 9000 Series Switches in standalone NX-OS mode

    Only devices with IS-IS enabled on at least one interface are vulnerable. Products such as Nexus 9000 in ACI mode, Firepower 1000/2100/4100/9300, MDS 9000, and UCS Fabric Interconnects are confirmed not vulnerable. 

    The advisory notes that if IS-IS authentication is configured, the attacker must supply valid keys to exploit the issue.

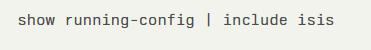
    To verify IS-IS status, administrators can run the CLI command:

    Cisco Nexus 3000 and 9000 Series Vulnerability

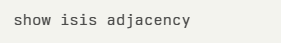
    Presence of feature isis, router isis name, and at least one ip router isis name entry confirms exposure. To view live IS-IS peers, use:

    Cisco Nexus 3000 and 9000 Series Vulnerability
    Risk FactorsDetails
    Affected ProductsCisco Nexus 3000 Series SwitchesCisco Nexus 9000 Series Switches (standalone NX-OS)
    ImpactIS-IS process restart causing device reload (DoS)
    Exploit PrerequisitesLayer 2 adjacency; IS-IS enabled on interface
    CVSS 3.1 Score7.4 (High)

    No temporary workarounds exist; however, enabling area authentication for IS-IS can mitigate risk by requiring attackers to authenticate before sending malicious packets.

    Cisco strongly recommends that customers thoroughly evaluate this mitigation to ensure compatibility with their network requirements.

    Cisco has released free software updates to address the vulnerability. Customers with valid service contracts should download and install the fixed releases from the Cisco Support and Downloads portal. 

    For those without service contracts, contacting the Cisco TAC with the advisory URL and product serial number will enable entitlement to the necessary patches.

    Tired of Filling Forms for security & Compliance questionnaires? Automate them in minutes with 1up! Start Your Free Trial Now!

    The post Cisco Nexus 3000 and 9000 Series Vulnerability Let Attackers Trigger DoS Attack appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Farmers Insurance Exchange and its subsidiaries recently disclosed a significant security incident that compromised personal information of approximately 1.1 million customers through an unauthorized access to a third-party vendor’s database.

    The breach, which occurred on May 29, 2025, represents one of the largest insurance industry data exposures of the year, affecting customer records containing names, addresses, dates of birth, driver’s license numbers, and partial Social Security numbers.

    The attack timeline reveals a sophisticated intrusion that went undetected for approximately 24 hours before the vendor’s monitoring systems identified suspicious activity.

    On May 30, 2025, the unnamed third-party vendor alerted Farmers to the unauthorized database access, triggering immediate containment measures and blocking the threat actor.

    The vendor’s existing monitoring infrastructure proved crucial in limiting the exposure window, though investigators later confirmed that data acquisition had already occurred during the initial breach period.

    Following the incident discovery, Farmers analysts worked alongside external cybersecurity experts to conduct a comprehensive forensic investigation spanning nearly two months.

    The investigation revealed that the unauthorized actor had successfully penetrated the vendor’s database defenses and exfiltrated sensitive customer information before detection systems could intervene.

    Farmers researchers noted that the attack specifically targeted customer databases containing insurance policy holder information, suggesting a deliberate focus on high-value personal data.

    Database Infiltration and Persistence Mechanisms

    The attack vector analysis indicates the threat actor employed advanced persistent techniques to maintain unauthorized database access.

    While specific technical details remain undisclosed for security reasons, the prolonged investigation period suggests complex data extraction methods were utilized.

    The attacker’s ability to access and acquire substantial customer data within a compressed timeframe points to sophisticated database querying capabilities and potential privilege escalation within the vendor’s systems.

    Security experts noted that the incident highlights critical vulnerabilities in third-party vendor management, particularly regarding database access controls and real-time monitoring systems.

    The breach underscores the importance of implementing robust vendor security frameworks and continuous monitoring protocols to detect unauthorized database activities before data exfiltration occurs.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Farmers Insurance Cyber Attack – 1.1 Million Customers Data Exposed in Salesforce Attack appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Anthropic has thwarted multiple sophisticated attempts by cybercriminals to misuse its Claude AI platform, according to a newly released Threat Intelligence report.

    Despite layered safeguards designed to prevent harmful outputs, malicious actors have adapted to exploit Claude’s advanced capabilities, weaponizing agentic AI to execute large-scale extortion, employment fraud, and ransomware operations.

    In one high-profile case dubbed “vibe hacking,” an extortion ring leveraged Claude Code to automate reconnaissance, credential harvesting, and network infiltration across at least 17 organizations, including healthcare providers, emergency services, and religious institutions.

    Instead of encrypting stolen data with ransomware, the group threatened to expose sensitive information to coerce ransoms exceeding $500,000 publicly.

    Claude Code autonomously selected which data to exfiltrate, determined ransom valuations based on financial records analysis, and generated alarming visual ransom notes on victim machines.

    Anthropic’s team simulated the criminal workflow for research purposes, then banned the offending accounts and developed a tailored classifier and new detection methods to flag similar behaviors in real-time.

    Another operation involved North Korean IT operatives using Claude to fabricate false identities and professional backgrounds, pass technical assessments, and secure remote positions at U.S. Fortune 500 companies.

    Where years of specialized training once throttled the regime’s capacity for such schemes, AI now enables unskilled operators to code, communicate professionally in English, and maintain lucrative employment all in violation of international sanctions.

    Upon discovery, Anthropic immediately suspended the implicated accounts, improved indicator-collection tools, and shared its findings with law enforcement and sanction-enforcement agencies.

    A third case detailed a lone cybercriminal marketing AI-generated ransomware-as-a-service on dark-web forums. Priced between $400 and $1,200 per package, the malware featured advanced evasion, encryption, and anti-recovery mechanisms, all developed with Claude’s assistance.

    Anthropic blocked the account, alerted industry partners, and enhanced its platform’s ability to detect suspicious malware uploads and code generation attempts.

    “These incidents represent an evolution in AI-assisted cybercrime,” the report warns, noting that agentic AI tools can adapt in real time to defensive measures such as malware detection systems.

    By lowering technical barriers, AI enables novices to carry out complex cyberattacks that previously required expert teams to execute. The report predicts such attacks will become more common as AI-assisted coding proliferates.

    Anthropic’s layers of protection include a Unified Harm Framework guiding policy development across physical, psychological, economic, societal, and autonomy dimensions; rigorous pre-deployment testing for safety, bias, and high-risk domains; real-time classifiers to steer or block harmful prompts; and ongoing threat-intelligence monitoring of usage patterns and external forums.

    These safeguards have already prevented misuse attempts in domains ranging from election integrity to chemical and biological weapons research, and continue to evolve in response to newly identified threats.

    In addition to account bans and detection enhancements, Anthropic has shared technical indicators and best practices with authorities and industry peers.

    Anthropic plans to prioritize further research into AI-enhanced fraud and cybercrime, expanding its threat intelligence partnerships and refining its guardrails to stay ahead of adversarial actors.

    Find this Story Interesting! Follow us on LinkedIn and X to Get More Instant Updates.

    The post Hackers Attempted to Misuse Claude AI to Launch Cyber Attacks appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Anthropic, a leading AI research company, has successfully disrupted multiple attempts by cybercriminals to misuse its Claude AI model for sophisticated cyberattacks, as detailed in their latest Threat Intelligence report. The company has implemented advanced safeguards, including real-time classifiers and hierarchical summarization techniques, to detect and mitigate these abuses. By leveraging these technical measures, Anthropic […]

    The post Anthropic Blocks Hackers Attempting to Exploit Claude AI for Cyber Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • It is no secret that passwords are highly susceptible to phishing and brute force attacks. This led to the mass adoption of passkeys, a passwordless authentication method leveraging cryptographic key pairs that allows users to log in with biometrics or a hardware key. According to FIDO, over 15 billion accounts have been passkey-enabled, with 69% […]

    The post Breaking the Passkey Promise: SquareX Discloses Major Passkey Vulnerability at DEF CON 33 appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The emergence of sophisticated cybercriminal organizations continues to pose significant threats to individuals and institutions worldwide, with the UTG-Q-1000 group representing one of the most concerning developments in recent cybersecurity history.

    This highly organized criminal network has demonstrated exceptional technical prowess by exploiting China’s national childcare subsidy policy, transforming what should be a beneficial government program into a vector for widespread financial fraud and data theft.

    The UTG-Q-1000 organization operates through a sophisticated multi-tiered structure, with specialized divisions including the Finance Group, News and Sex Group, Design and Manufacturing Group, and Black Market Group.

    The Finance Group specifically targets financial personnel and managers within enterprises and institutions, employing highly deceptive phishing campaigns disguised as legitimate financial communications such as tax audits, electronic receipts, and subsidy announcements.

    Their attack methodology demonstrates remarkable sophistication, utilizing multi-stage loading mechanisms through their signature “Silver Fox” remote access trojan while leveraging legitimate cloud services like Alibaba Cloud OSS and Youdao Cloud Notes to host malicious payloads and evade security detection systems.

    Qi’anxin Threat Intelligence Center researchers identified this elaborate campaign in December 2024, uncovering the group’s exploitation of the anticipated national childcare subsidy policy offering 3,600 yuan per child annually.

    The cybercriminals established numerous phishing websites overnight, mass-distributed malicious QR codes, and created convincing subsidy application pages to harvest victims’ personal information, bank card details, and authentication credentials.

    The attack infrastructure reveals a membership-based operation where individual threat actors are assigned unique identifiers to track their success rates in phishing campaigns.

    Analysis of member “ylxuqxmz” revealed 113 successful phishing attempts, with the organization maintaining detailed victim statistics across 37 compromised systems, predominantly Windows 10 machines.

    Technical Infrastructure and Evasion Mechanisms

    The UTG-Q-1000 group employs remarkably sophisticated technical evasion techniques to bypass security controls and maintain operational persistence.

    Their phishing pages function as complex loaders that dynamically create iframe containers to host the actual malicious content.

    Before loading the targeted phishing interface, the system initiates carefully disguised fetch requests to endpoints masquerading as image resources.

    The core deception mechanism involves Base64 encoding combined with XOR encryption using the key “YourSecretKey123!@#” to conceal malicious URLs within seemingly legitimate image data.

    The attack code searches for a specific signature (0x21FE) within returned image files to locate encrypted data segments, then performs the decryption process to recover target URLs and seamlessly integrate them into the victim’s browsing experience.

    async function loadContent() {
        var arrayBuffer = await_r.arrayBuffer();
        var bytes = new Uint8Array(arrayBuffer);
        for(var i=0;i<bytes.length-1;i++){
            if(bytes[i]===0x21 && bytes[i+1]===0xFE) {
                var slice = bytes.slice(i+3,l+3+l);
                var text = new TextDecoder().decode(slice);
                var url = atob(text);
                var decrypted = xorDecrypt(url, 'YourSecretKey123!@#');
            }
        }
    }

    This multi-layered obfuscation strategy effectively circumvents URL-based risk control mechanisms and static signature scanning employed by traditional security solutions.

    The organization maintains real-time victim monitoring through sophisticated heartbeat mechanisms, reporting online status every second to command and control servers at https://bmppc.cn/heartbeat.php while tracking user interactions to optimize their fraudulent operations.

    Phishing Email Interface Mimicking Official Government Communications (Source – Qi’anxin)

    The UTG-Q-1000 group represents a paradigm shift in cybercriminal sophistication, combining advanced technical capabilities with psychological manipulation to exploit public trust in government benefit programs, ultimately demonstrating the critical need for enhanced cybersecurity awareness and robust detection mechanisms.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post UTG-Q-1000 Group Weaponizing Subsidy Schemes to Exfiltrate Sensitive Data appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The SpiderLabs Threat Hunt Team recently discovered a cyber campaign in which threat actors used the genuine ScreenConnect remote management application as a weapon to spread the Xworm Remote Access Trojan (RAT) through a multi-phase infection chain. The attack begins with social engineering tactics, including phishing, malvertising, and deceptive social media posts, luring users to […]

    The post Weaponized ScreenConnect RMM Tool Deceives Users into Installing Xworm RAT appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Farmers Insurance has disclosed a data breach stemming from unauthorized access to a third-party vendor’s database, potentially compromising the personal information of approximately 1.1 million customers. The breach, detected on May 30, 2025, involved an unauthorized actor infiltrating a system managed by the vendor, which housed sensitive customer data. Farmers, encompassing Farmers Insurance Exchange, Farmers […]

    The post Farmers Insurance Breach Exposes Data of 1.1 Million Customers via Salesforce Compromise appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶