• A critical security vulnerability affecting Apache DolphinScheduler’s default permission system has been identified and patched, prompting urgent update recommendations from the Apache Software Foundation.

    The vulnerability, which stems from overly permissive default configurations in the popular workflow scheduling platform, allows unauthorized users to execute arbitrary workflows and access sensitive system resources without proper authentication controls.

    The flaw emerged through the platform’s initialization process, where default administrative privileges were inadvertently granted to newly created user accounts.

    This architectural oversight created significant attack vectors for malicious actors seeking to compromise data processing pipelines and execute unauthorized code within enterprise environments.

    Organizations utilizing DolphinScheduler for critical workflow automation face immediate exposure to data exfiltration and system compromise.

    Initial reports indicate that the vulnerability has already been exploited in limited instances, with attackers leveraging the permission bypass to inject malicious workflows into production environments.

    Apache analysts identified the vulnerability during routine security auditing procedures, discovering that the default user role assignment mechanism failed to properly restrict administrative functions.

    Exploitation Mechanism and Code Analysis

    The vulnerability exploits a flaw in the user authentication module where default permissions are assigned through the following problematic code pattern:

    public void createDefaultUser() {
        User defaultUser = new User();
        defaultUser.setUserType(UserType.ADMIN_USER);
        defaultUser.setPermissions(Permission.ALL);
        userMapper.insert(defaultUser);
    }

    This initialization routine automatically assigns administrative privileges without validating user credentials or implementing proper access controls.

    Attackers can exploit this by creating new accounts during system initialization phases, effectively gaining unrestricted access to workflow management functions and underlying system resources.

    The Apache development team has released version 3.2.1 with enhanced permission validation and secure-by-default configurations, addressing the root cause of this critical security flaw.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Apache DolphinScheduler Default Permissions Vulnerability Fixed – Update Now appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The U.S. District Court for the District of Columbia has ordered Google to share critical search data with competitors while allowing the tech giant to retain ownership of its Chrome browser.

    The decision, announced Tuesday by the Department of Justice’s Antitrust Division, represents a significant victory in the government’s ongoing battle against Google’s search monopoly that has dominated the market for over a decade.

    The court’s remedies target Google’s anticompetitive practices without requiring the dramatic step of forcing a Chrome sale. Instead, the ruling focuses on breaking down the exclusionary agreements that have locked competitors out of the search market.

    Google will be prohibited from maintaining exclusive contracts relating to the distribution of Google Search, Chrome, Google Assistant, and the Gemini app across devices and platforms.

    Under the new requirements, Google cannot condition licensing agreements on the placement of its search products or tie revenue-sharing payments to maintaining Google Search as the default option for more than one year.

    The Justice Department’s Antitrust Division analysts noted that these practices created a “self-reinforcing cycle of monopolization” that effectively shut out potential competitors while reducing innovation and consumer choice.

    The most technically significant aspect of the ruling involves mandatory data sharing provisions.

    Google will be required to make certain search index and user-interaction data available to qualified competitors, fundamentally altering the competitive landscape.

    This data sharing requirement addresses one of the primary barriers competitors face when attempting to develop alternative search engines.

    # Example of potential API structure for mandated data access
    class SearchDataAPI:
        def get_search_index(self, query_parameters):
            # Return anonymized search index data
            pass
    
        def get_user_interaction_metrics(self, competitor_id):
            # Provide aggregated user behavior patterns
            pass

    Additionally, Google must offer search and search text ads syndication services to enable rivals to deliver competitive search results.

    This syndication requirement effectively opens Google’s advertising infrastructure to competitors, allowing them to build their own capacity while leveraging Google’s existing technology.

    The ruling stems from a case filed during President Trump’s first term in October 2020, ultimately supported by 49 states, two territories, and the District of Columbia.

    Following a nine-week bench trial in 2023 and a 15-day remedies trial in May 2025, the court concluded that Google violated Section 2 of the Sherman Act by maintaining its monopoly through anticompetitive practices that controlled approximately 90 percent of all U.S. search queries.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Google Won’t Be Forced to Sell Chrome, But Must Share Search Data With Rivals appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated backdoor linked to the notorious Russian cyber-espionage group APT28 allows attackers to exfiltrate data, upload files, and execute commands on compromised computers.

    The new, sophisticated backdoor targets Microsoft Outlook, which allows threat actors to steal data and take control of a victim’s machine.

    The malware, dubbed “NotDoor,” has been attributed to the Russian state-sponsored cyber threat group APT28, also known as Fancy Bear. LAB52 published the findings, the threat intelligence unit of Spanish cybersecurity firm S2 Grupo.

    NotDoor is a stealthy malware written in Visual Basic for Applications (VBA), the scripting language used to automate tasks within Microsoft Office applications.

    The backdoor is designed to monitor a victim’s incoming emails for specific trigger words, such as “Daily Report.” When an email containing the trigger is detected, the malware activates, enabling attackers to execute malicious commands.

    The name ‘NotDoor’ was coined by researchers due to the use of the word ‘Nothing’ within the malware’s code.

    ‘NotDoor’ Malware Attacks Outlook Users

    The malware cleverly abuses legitimate Outlook features to remain hidden and maintain persistence. It uses event-driven VBA triggers, such as Application_MAPILogonComplete, which runs when Outlook starts, and Application_NewMailEx, which is activated upon the arrival of a new email, S2 Grupo said.

    To evade detection by security software, NotDoor employs several sophisticated techniques:

    • Code Obfuscation: The malware’s code is intentionally scrambled with randomized variable names and a custom encoding method to make analysis difficult.
    • DLL Side-Loading: It uses a legitimate, signed Microsoft binary, OneDrive.exe, to load a malicious DLL file. This technique helps the malware appear as a trusted process.
    • Registry Modification: For persistence, NotDoor alters Outlook’s registry settings. It disables security warnings about macros and suppresses other prompts, allowing it to run silently without alerting the user.

    Once active, the backdoor creates a hidden directory to store temporary files, which are then exfiltrated to an attacker-controlled email address (a.matti444@proton[.]me) before being deleted. The malware confirms its successful execution by sending callbacks to a webhook site.

    APT28 is a well-known threat actor linked to Russia’s General Staff Main Intelligence Directorate (GRU). Active for over a decade, the group has been responsible for numerous high-profile cyberattacks, including the 2016 breach of the Democratic National Committee (DNC) during the U.S. presidential election and intrusions into the World Anti-Doping Agency (WADA).

    This new tool demonstrates the group’s continuous evolution and its ability to develop new methods to bypass modern defense mechanisms.

    According to S2 Grupo, the NotDoor malware has already been used to compromise multiple companies across various sectors in NATO member countries.

    To defend against this threat, security experts recommend that organizations disable macros by default across their systems, closely monitor for any unusual activity within Outlook, and inspect email-based triggers that could be exploited by such malware.

    Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant Updates.

    The post New ‘NotDoor’ Malware Attacks Outlook Users to Exfiltrate Data and Compromise Computers appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated new backdoor malware has emerged from the shadows, operating undetected for over 20 months while infiltrating networks through an ingenious dual-mode activation system.

    Initially discovered masquerading as a Mirai variant, MystRodX represents a significant evolution in stealth malware design, utilizing DNS queries and ICMP packets as covert communication channels to evade traditional security measures.

    ICMP packet (Source – XLab)

    The malware first surfaced on June 6, 2025, when suspicious activity was detected from IP address 139.84.156.79 distributing an ELF file named dst86.bin.

    Despite conventional scanners classifying it as Mirai with only a 4/65 detection rate on VirusTotal, the threat proved to be entirely different from known Mirai strains.

    XLab’s Cyber Threat Insight and Analysis System analysts identified the true nature of this threat through advanced behavioral analysis, revealing a complex C++ backdoor with unprecedented stealth capabilities.

    What sets MystRodX apart is its passive operational mode, where the malware can remain completely dormant without binding to network ports, making it virtually invisible to standard network monitoring tools.

    The threat operates through a sophisticated triple-layer encryption strategy, employing single-byte XOR for VM detection strings, custom transform algorithms for AES keys and trigger packets, and AES CBC mode for configuration data.

    This multi-tiered approach ensures that sensitive components remain protected even if portions of the malware are discovered.

    The malware’s configuration reveals activation timestamps dating back to January 7, 2024, indicating extensive deployment across compromised systems.

    Specified protocol (Source – XLab)

    Three active command-and-control servers have been identified in the wild, with evidence suggesting additional undiscovered campaigns utilizing distinct RSA key pairs for different attack operations.

    DNS-Based Activation Mechanism

    MystRodX’s most innovative feature lies in its DNS-triggered activation system, which transforms seemingly benign DNS queries into sophisticated command vectors.

    The malware monitors incoming network traffic using raw sockets, analyzing DNS requests that follow the specific format: www.DomainName.com, where the domain name contains encoded activation instructions.

    The activation process begins when the malware encounters a DNS query containing a specially crafted domain.

    For example, a domain like “www.UBw98KzOQyRpoSgk5+ViISKmpC6ubi7vao=.com” serves as the trigger mechanism.

    The encoded portion undergoes Base64 decoding, producing a 32-byte ciphertext that contains the activation payload.

    MagicString (Source – XLab)

    Using a proprietary transform algorithm with predefined magic values (0x0d and 0xaa), the malware decrypts this payload to reveal critical operational parameters including the magic identifier “CAT”, protocol specification (TCP/HTTP), target port number, and command-and-control server IP address.

    # Transform algorithm implementation
    def transform(magic, magic2, buf, key):
        buf_len = len(buf) - 1
        key_len = len(key)
        key1 = magic ^ calc_sum(key)
        key2 = (key[(key1^buf_len)%key_len]) ^ magic2 ^ buf_len
    
        out = bytearray()
        for i, value in enumerate(buf):
            out.append((key[(i^key1)%key_len] ^ key2 ^ value ^ i) & 0xff)
        return out

    Once successfully activated, MystRodX establishes communication with the specified command-and-control infrastructure, transitioning from its passive surveillance state to an active backdoor capable of file management, reverse shell operations, SOCKS proxy functionality, and port forwarding capabilities.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post MystRodX Leveraging DNS and ICMP to Steal Sensitive Data From Hacked Systems appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated phishing operation has been running undetected for over three years across Google Cloud and Cloudflare infrastructure, impersonating major corporations including defense contractor Lockheed Martin.

    The campaign, which utilized advanced cloaking techniques and compromised expired domains, demonstrates a concerning failure in detection capabilities by two of the internet’s largest service providers.

    The operation began with attackers acquiring expired domains that previously belonged to legitimate organizations, then deploying cloned websites of Fortune 500 companies.

    The scheme specifically targeted high-value domains with established reputations and active social media communities, making the impersonations more convincing to unsuspecting users.

    One notable case involved the domain militaryfighterjet.com, which originally hosted content about military aircraft but was transformed into a gambling site that simultaneously served as a perfect clone of Lockheed Martin’s corporate website.

    Clone of Lockheed Martin’s site (Source – Medium)

    The attackers employed sophisticated cloaking technology that presented different content based on the visitor’s user agent and geographic location.

    When accessed by search engine crawlers or through Google search results, users would see legitimate-looking clones of corporate websites.

    However, direct browser access revealed gambling content, creating a dual-purpose infrastructure that evaded automated detection systems while serving illicit content to real users.

    Deep Specter Research analysts identified this massive operation through their investigation of the militaryfighterjet.com domain transformation.

    Their analysis revealed that the infrastructure comprised over 48,000 active virtual hosts organized into 86 distinct clusters, with the majority hosted on Google Cloud platforms in Hong Kong and Taiwan.

    The researchers discovered evidence of the operation dating back to 2021, with significant expansion periods coinciding with major cybersecurity incidents and data breaches worldwide.

    Technical Infrastructure and Attack Methodology

    The campaign’s technical sophistication becomes apparent when examining the underlying infrastructure and deployment methods.

    Deep Specter Research analysts noted that the attackers utilized HTTrack Website Copier, a legitimate web scraping tool, to create pixel-perfect replicas of target organizations’ websites.

    Evidence of this tool’s usage was found embedded in the HTML comments of cloned sites, including timestamps showing when specific sites were copied.

    The operation’s source code analysis revealed strategic implementation details that made detection particularly challenging.

    The cloaking system examined HTTP headers, user agent strings, and IP geolocation data to determine whether visitors were legitimate users, search engine bots, or security researchers.

    Gambling content (Source – Medium)

    This selective content delivery allowed the malicious sites to maintain high search engine rankings while serving gambling content and potential malware to targeted demographics.

    The infrastructure demonstrated remarkable resilience and scalability, with attackers maintaining over 200 cloned brands across multiple industries including military, healthcare, and manufacturing sectors.

    The largest single cluster contained nearly 6,000 virtual hosts serving cloned content of a single organization, suggesting this may represent preparation for a large-scale breach campaign.

    Analysis of the network architecture revealed eight upper-tier management hosts coordinating 78 regular cluster managers, indicating a hierarchical command structure typical of professional cybercriminal operations.

    The attackers strategically leveraged the trusted nature of Google Cloud and Cloudflare infrastructure to bypass security filters and maintain persistence across their extensive network of compromised domains.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Phishing Campaign Went Undetected for Over 3 Years on Google Cloud and Cloudflare appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The maker of F-35 jets is getting paid for on-time delivery, even though it’s not delivering the aircraft on time and without the required upgrades, a government watchdog agency said. 

    “The F-35 program office compensated Lockheed Martin with hundreds of millions of dollars of performance incentive fees while the percentage of aircraft delivered late and the average days late grew,” according to a new report from the Government Accountability Office.  

    Both Lockheed and engine-builder Pratt & Whitney have received incentive fees, but the money has been “largely ineffective” at holding the contractors accountable, according to GAO. The structure of the incentives has allowed Lockheed to deliver F-35s “up to 60 days late” and earn some of the money. 

    “Unless the F-35 program re-evaluates its use of incentive fees and better aligns them to achieving desired production schedule outcomes, it will be at greater risk of continuing to reward contractors for delivering engines and aircraft late,” GAO said. 

    In a statement, Lockheed said it is “dedicated to meeting our customer requirements and delivering on our commitments. We are investing in mission-driven business and digital transformation to ensure we’re able to deliver capability at the speed of relevance.” 

    The report outlined fresh delays with the program’s Block 4 modernization effort and Technology Refresh 3 upgrade—the backbone of Block 4. The program has reduced the amount of capabilities it will deliver with Block 4 as costs have ballooned from $10.6 billion to $16.5 billion, according to an estimate from 2021. (GAO noted that the program does not have an updated cost estimate for Block 4).   

    The reduced set of Block 4 capabilities won’t be finished till 2031—5 years later than the program originally expected to finish the whole Block 4 effort, the report said.

    “According to program officials, the new Block 4 major subprogram will have fewer capabilities, will experience schedule delays, and will have unknown costs until the program office finishes developing its cost estimate,” GAO said. 

    Specifically, the program will delay Block 4 capabilities that require an upgraded engine to work. The effort, called Engine Core Upgrade, was designed to improve the engine’s performance and provide the necessary power for Block 4, but the upgrade has been delayed and production for ECU won’t start until 2031, the report said.

    The jet’s cooling system also needs to be upgraded to handle more cooling beyond Block 4, but production of that upgrade, known as PMTU, won’t start until 2033, the report said.

    In order for Block 4 to work, the program has to finish TR-3—a $1.9 billion software and hardware upgrade that was supposed to be ready in April 2023. In June of this year, Lockheed executives announced the company had finished a combat-capable version of TR-3, but GAO said TR-3 won’t be fully ready until next year. GAO did say that the program plans to begin updating some F-35s with “limited” combat-capable software in July 2025.

    “According to program officials, Lockheed Martin plans to begin delivering combat-capable aircraft with TR-3 that will enable Block 4 capabilities in 2026, a 3-year delay due to hardware and software issues,” GAO said. 

    Asked about GAO’s date for TR-3, Lockheed said it has completed all “TR-3 hardware and software configurations that support the TR-3 contract including design, build and testing.”

    Chronic delays and cost overruns led the Pentagon to stop accepting new F-35s for a year—a pause that ended in July 2024. Since then, the Pentagon has been accepting TR-3 jets with a “truncated” version of the TR-3 package.

    GAO attributed the TR-3 delays to problems with software stability, quality issues and late deliveries with the integrated core processor, and delays with a new suite of sensors, called the Next Generation Distributed Aperture System. 

    Program officials said the new core processor isn’t causing TR-3 delays anymore, but the new aperture system won’t be done until 2026, “making it a key driver for TR-3-enabled capability delays,” GAO said. 

    The F-35 program office did not respond to a request for comment in time for publication. 

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Computers with components made of diamond are being installed at Oak Ridge National Laboratory in Tennessee in a bid to marry quantum information technologies with classical computers, the lab announced on Tuesday. 

    Quantum science promises advances in fields from cryptography to chemistry, but realizing that promise depends on finding a way to connect quantum and classical systems. 

    “By hosting a Quantum Brilliance system on site, we’ll be maturing the real mechanics of hybrid computing — co‑scheduling, end‑to‑end performance tuning, data and workflow orchestration, workforce development and more — so we can eventually move HPC-quantum integration from a conceptual pilot to a fully embedded capability within leadership computing,” said Ashley Barker, who directs Oak Ridge's Leadership Computing Facility Program. 

    Quantum Brilliance’s products use synthetic diamonds to ease the challenges of today's quantum systems, such as external noise that introduces errors into quantum calculations.

    “Diamond is extremely hard, so even at room temperature and atmospheric pressure, there isn’t sufficient thermal energy to generate the vibrations that would typically disrupt qubit coherence,” said CEO Mark Luo. “This intrinsic stability allows our QPUs to function without the complexity and cost of cryogenics, laser and vacuum systems. This allowed us to engineer a revolutionary QPU solution that operates efficiently at room temperature while dramatically reducing size, weight and power consumption.”

    Oak Ridge is among the national labs working on quantum systems with companies and other federal entities.

    ]]>

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Cybersecurity researchers have discovered two new malicious packages on the npm registry that make use of smart contracts for the Ethereum blockchain to carry out malicious actions on compromised systems, signaling the trend of threat actors constantly on the lookout for new ways to distribute malware and fly under the radar. “The two npm packages abused smart contracts to conceal malicious

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent advisory warning about a critical vulnerability in SunPower PVS6 solar power devices that could allow attackers to gain complete control over the systems.

    The flaw, tracked as CVE-2025-9696, stems from the use of hardcoded credentials in the device’s BluetoothLE interface, presenting a significant threat to solar energy infrastructure worldwide.

    The vulnerability affects SunPower PVS6 versions 2025.06 build 61839 and prior, with a CVSS v4 score of 9.4, indicating its critical severity.

    Attackers positioned within Bluetooth range can exploit this weakness to access the device’s servicing interface, enabling them to replace firmware, disable power production, modify grid settings, create SSH tunnels, alter firewall configurations, and manipulate connected devices.

    CISA analysts identified that the vulnerability exploits hardcoded encryption parameters and publicly accessible protocol details within the BluetoothLE implementation.

    This design flaw transforms what should be a secure maintenance interface into an open gateway for malicious actors. The attack vector requires only adjacent network access with low complexity, making it particularly concerning for solar installations in populated areas.

    Technical Attack Mechanism and Exploitation

    The vulnerability leverages the inherent weakness in the PVS6’s authentication system, where static credentials provide a consistent entry point for attackers.

    Once an attacker establishes a Bluetooth connection using these hardcoded parameters, they gain administrative privileges equivalent to legitimate service personnel.

    The exploitation process involves reverse-engineering the publicly available protocol documentation to identify the authentication sequence.

    # Simplified representation of the vulnerability
    bluetooth_connection = establish_ble_connection(target_device)
    if authenticate_with_hardcoded_key(DEFAULT_SERVICE_KEY):
        admin_access = True
        execute_firmware_replacement()
        modify_power_settings()

    The attack’s sophistication lies in its simplicity – no complex exploits or zero-day techniques are required.

    Attackers can potentially develop automated tools to scan for vulnerable devices and compromise them systematically.

    The vulnerability’s impact extends beyond individual devices, as compromised units could serve as pivots to access broader energy infrastructure networks.

    Notably, SunPower has not responded to CISA’s coordination attempts, leaving users without official patches.

    CISA recommends implementing network isolation, using VPNs for remote access, and deploying comprehensive monitoring systems to detect unauthorized access attempts.

    Organizations should prioritize updating affected devices once patches become available and consider temporarily disabling Bluetooth functionality where operationally feasible.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post CISA Warns of Critical SunPower Device Vulnerability Let Attackers Gain Full Device Access appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Binance, the world’s largest cryptocurrency exchange by volume, continues to hit new milestones, with regards to the platform’s active user base. For example, Binance recently hit the 275 million registered users milestone.

    However, where Binance may be really knocking it out of the park, in terms of hitting userbase milestones, may be with the company’s mobile platform.

    For instance, last September, Binance was not just the most widely-downloaded crypto app; it was the most widely-downloaded finance app, with 9.9 million downloads during that month.

    Specifically, thanks to the continued success of Binance mobile, the company’s goal of reaching 1 billion users seems less far-fetched than before.

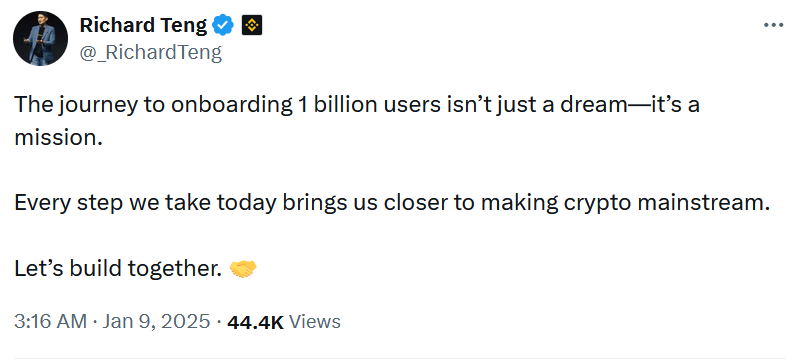
    As Binance CEO Richard Teng noted in an X post published earlier this year, “the journey to onboarding 1 billion users isn’t a dream—it’s a mission. Every step we take today brings us closer to making crypto mainstream. Let’s build together.”

    Binance Mobile App: Adapting to Changing Preferences, While Attracting the Masses

    So far, over 100 million Binance members have downloaded the mobile version, with 75% of members utilizing the mobile app. This is not surprising.

    Much like how stock trading has moved from desktop-based platforms to mobile brokerage apps, the same trends are playing out in the cryptocurrency space.

    At same time, while Binance is catering to changing trading habits among experienced users, the launch of the mobile application has made Binance a more accessible and convenient platform for those new to the crypto game. This has been very beneficial in terms of membership growth.

    As cryptocurrency goes mainstream, and an increasing share of the global population join the crypto community, Binance is one of the top beneficiaries of this expanding market.

    Last year, over 68 million new users signed up for Binance. That’s an average of 187,000 new users per day. Consumer assets on the platform also increased by a staggering 92.9%, climbing to $73.1 billion.

    More Than Just Trading

    Although Binance users may initially join in order to buy and sell cryptocurrencies, in time they quickly realize that there’s more to Binance than just its exchange.

    However, while Binance’s security, speed, and low transaction cost advantages may be what initially attracts users, something else helps to retain them as active users.

    Yes, the high-quality of the Binance platform itself, including the platform’s user-friendly interface, do wonders in terms of keeping users engaged and motivated to use the platform.

    However, what likely keeps users from moving to different platforms is the wide variety of Web3 products, services, and functionalities that are within the Binance ecosystem.

    With the Binance platform, users are able to do more than just make crypto trades. Through Binance Earn, members can earn a yield on their cryptocurrency assets.

    Binance Pay enables users to securely complete crypto-based payment transactions. Via Binance’s Web3 wallet feature, members are able to access the myriad of CeFi, DeFi, and dApps that have become a key feature of the Web3 economy.

    These additional features may not be what brought new users to the platform in the first place, but they are material in keeping them actively engaged with the platform. In turn, this points to limited membership churn, and in turn, continual growth of Binance’s user base.

    Next Stop 1 Billion Users

    Over 100 million Binance members now utilize the mobile app, but in time this figure could grow many times over. Soon, the mobile application could hit 250 million, 500 million, even 1 billion users.

    Yes, at first this may sound like a tall order. However, keep in mind that the number of crypto owners worldwide now totals over 500 million.

    More importantly, keep in mind that 6 billion people, around 70% of the world’s population, use mobile devices. In short, mobile applications stand to be the most accessible way for current non-users to make the first step in their respective cryptocurrency journeys.

    As crypto goes mainstream, to the point where a greater share of everyday transactions are conducted on chain rather than through the traditional banking system, access to crypto platforms will become essential.

    In turn, as having a cryptocurrency account becomes as common as owning a mobile device, this ever-growing pool of crypto users will likely choose the safest, most reliable and most user-friendly platform out there. Hence, it’s not far-fetched to imagine Binance’s mobile app growing tenfold in the years to come.

    The post Binance Hits 100M+ App Downloads: A Milestone Powering Crypto’s Global Reach appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶